Article
Binance Hack 2026: What Happened and Why It Matters
Imagine you use a crypto exchange. You create a strong password, enable two-factor authentication and avoid suspicious links.
You have done your part. So your funds should be safe, right?
Your login can be well protected while the company holding your assets has a different problem. That is the uncomfortable part of trusting someone else with custody.
The recent Binance hack is worth understanding for that reason. Not just because the number is enormous, but because it raises questions that matter to anyone building an application people trust.
Reporting checked on October 31, 2026. This is a developing investigation, not a final technical post-mortem.
What happened in the Binance hack?
In its October 30 second update, Binance said its hot wallets were compromised at around 20:05 UTC on October 29, 2026, with approximately $6.3 billion in token assets stolen. (Binance's second update)
The company's second update also reported: (Binance's second update)
- Approximately $3 billion frozen on-chain.
- A commitment to cover the stolen funds using its SAFU protection fund and corporate treasury.
- More than $6.34 billion in company funds set aside, with $5 billion held in the same token assets that were stolen.
- Suspended withdrawals, with a phased restart targeted after security checks rather than an unconditional reopening promise.
- An ongoing investigation, with no evidence of leaked wallet private keys found at that stage.
These are Binance's statements about its response and replacement funding, not an independent verification of reserves. Setting aside company funds is different from recovering stolen assets. Frozen assets are not automatically assets returned to their owner, either.
Those differences matter when billions of dollars are involved. They also matter when it is your savings.
Was it really just one engineer's laptop?
Binance's initial explanation suggested a compromised DevOps engineer's laptop may have allowed access to a service container and unauthorized withdrawal transactions. (Binance's initial update)
That quickly becomes a simple headline: one laptop, billions gone.
But the later update said investigators had uncovered additional points of breach. The complete attack sequence was still being established. (Binance's second update)
So no, we should not pretend the entire incident has already been explained. We also should not invent a story about an engineer clicking a particular link, downloading a particular file or using a particular AI tool.
There is a useful engineering question here, though:
If one trusted device or service is compromised, how far should that access be allowed to travel?
That question applies to a crypto exchange. It also applies to your small Next.js app with a production dashboard open in another tab.
How can funds move without a leaked private key?
This is where the story becomes more interesting than “someone stole a password.”
Imagine a company safe. One attack is stealing the key. Another is gaining control of the process that tells the authorized employee to open it.
The key may never leave the building. The outcome can still be terrible.
TRM Labs' on-chain analysis reported valid signed transfers across multiple blockchains and assessed that Binance's hot-wallet signing infrastructure was likely compromised. That is a research assessment, not a completed Binance root-cause report. (TRM Labs)
For a reader who does not live inside blockchain terminology: a hot wallet is an online wallet used for operations such as withdrawals. The signing system authorizes transactions from it. (TRM Labs)
Protecting a secret key is essential. Protecting what can ask that key to authorize is essential too.
You do not make a bank safe by guarding the vault key while accepting any instruction written on company letterhead.
EIP-7702, without the headache
TRM also reported that the attacker used an EIP-7702 delegation on an Ethereum hot wallet, directing it to attacker-controlled code that could sweep funds. Its report described ordinary signed transfers on other chains, not one Ethereum mechanism explaining everything. (TRM Labs)
What does that mean?
Ethereum's EIP-7702 lets an ordinary account authorize smart-contract code to run in its account context. The account can gain programmable behavior without the user simply creating an entirely separate smart-contract wallet. (Ethereum.org)
Think of granting an assistant permission to act through your account. The important questions become: Which assistant? What code? What authority?
That can be useful. It also means an authorization deserves more attention than “the wallet showed a signature button.”
This is not evidence that Ethereum's cryptography suddenly stopped working, or that every wallet using the feature is compromised. It is a reminder to distinguish a valid signature from an action the real owner intended.
The lesson for developers is bigger than crypto
You may be reading this thinking:
I build websites. I do not operate a billion-dollar exchange.
Fair enough. Your application may not sign crypto withdrawals. But imagine the following setup:
Your laptop can deploy production. The deployment pipeline can read secrets. A service account can export customer records. An admin panel can change payment destinations.
Now ask what happens if an attacker gets control of the wrong account, device or service.
This is a hypothetical architecture example, not a claim that Binance used this exact setup.
The point is that your security boundary is not just the login screen your customers see. It includes the people, devices and services behind it.
A beautiful dashboard is not an access-control policy. Neither is dark mode, although apparently we keep trying.
What I would check in an application I am responsible for
These are practical design checks, not a claim that any one of them would have prevented this particular incident.
1. Reduce what each credential can do
A deployment credential should not quietly become permission to operate every sensitive business function. Review permissions by actual need, not by what was convenient during setup.
OWASP's secrets-management guidance emphasizes restricted access and least privilege. Start there before buying another dashboard that promises to solve security for you. (OWASP secrets guidance)
2. Keep secrets short-lived and revocable
Where supported, use short-lived credentials instead of permanent secrets copied between developer machines, pipelines and servers. Have an explicit way to revoke compromised access at the service that accepts it. (OWASP secrets guidance)
Restarting your app is not the same as revoking a stolen credential. The attacker is not politely waiting for your next deployment. (OWASP secrets guidance)
3. Protect privileged access beyond a password
Use phishing-resistant authentication where supported, including properly implemented passkeys or security keys. Protect recovery and factor-reset processes too; a weak recovery path can undermine a strong login. (OWASP MFA guidance)
And remember what that control is protecting. Strong authentication for one person's account does not, by itself, validate every later instruction inside a company.
4. Make high-risk authority explicit
Ask whether one compromised service can change a payout destination and authorize the payout. Consider independent approvals, narrowly scoped signing policies and limits appropriate to the business risk.
For crypto treasury teams specifically, TRM recommends rejecting unexpected EIP-7702 authorizations and separating signing infrastructure and approval paths by chain and wallet tier. (TRM Labs)
The useful question is not “Do we have approvals?” It is “Can the same compromised path satisfy all of them?”
5. Rehearse the response
Can you revoke access quickly? Can you identify which credentials were exposed? Are the relevant logs available without recording the secrets themselves?
OWASP treats rotation, revocation and auditing as parts of a secret's lifecycle, not chores to invent during an incident. (OWASP secrets guidance)
An emergency is a bad time to discover that the only person who knows the recovery procedure is on a flight.
What should ordinary users take from this?
Do not turn a developing incident into a panic-driven instruction to buy, sell or move assets somewhere you do not understand.
Instead:
- Check official updates directly. Use the app or a known official address, not a “recovery” link in an unsolicited message. Binance itself directs users to its official channels. (Binance's initial update)
- Keep your own account protected. Strong authentication and careful account recovery still matter, even though they do not eliminate a custodian's infrastructure risk. (OWASP MFA guidance)
- Separate promises from completed outcomes. A recovery plan, an asset freeze and a restored service are different milestones. Read the actual status rather than a reassuring screenshot.
The right question is not simply whether a platform says security is important. It is what evidence supports its claims, what risks you are accepting and what happens when a control fails.
The uncomfortable takeaway
For developers, the Binance hack is a reason to look beyond the customer-facing application. Ask about privileged devices, service identities and the systems authorized to act on customers' behalf.
For users, it is a reminder that a strong personal password cannot eliminate every risk at a company holding your assets.
Neither lesson requires us to pretend the investigation is finished.
Your application is more than the code you deploy. It is also everyone and everything you allow to act with its authority.
This article is security commentary, not investment advice. Findings and operational status may change as the investigation develops.
Read next
View all articles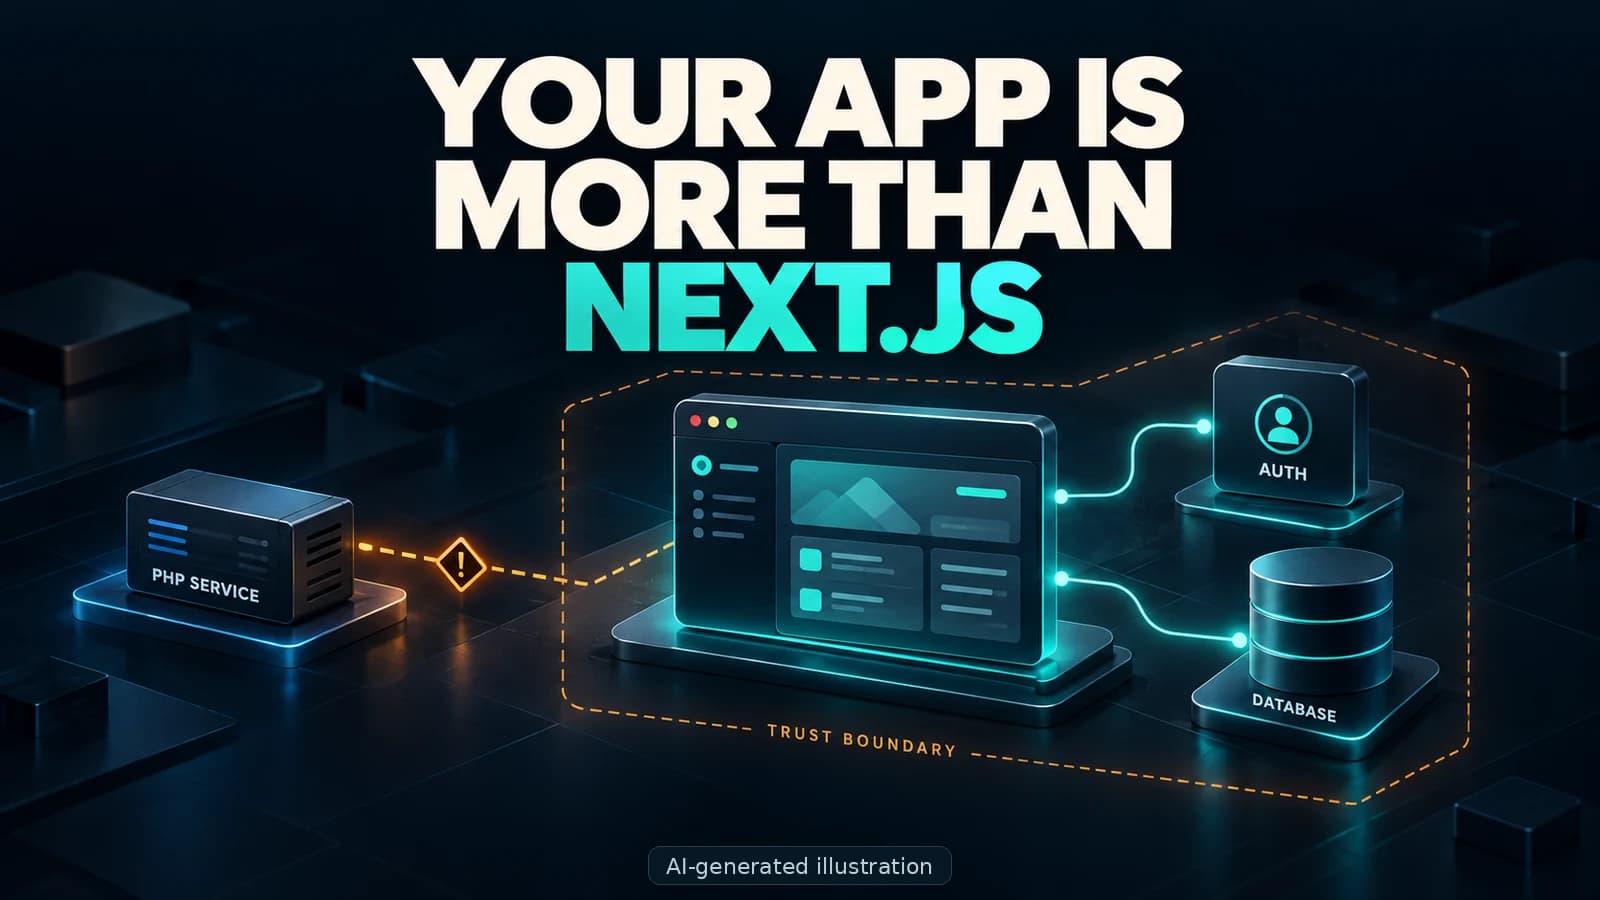
Can a PHP Shell Affect Your Next.js or MERN App?
Learn how a PHP shell can affect a Next.js or MERN app, where tools like Appwrite and Clerk fit, and how to protect your database and customer data.
Read more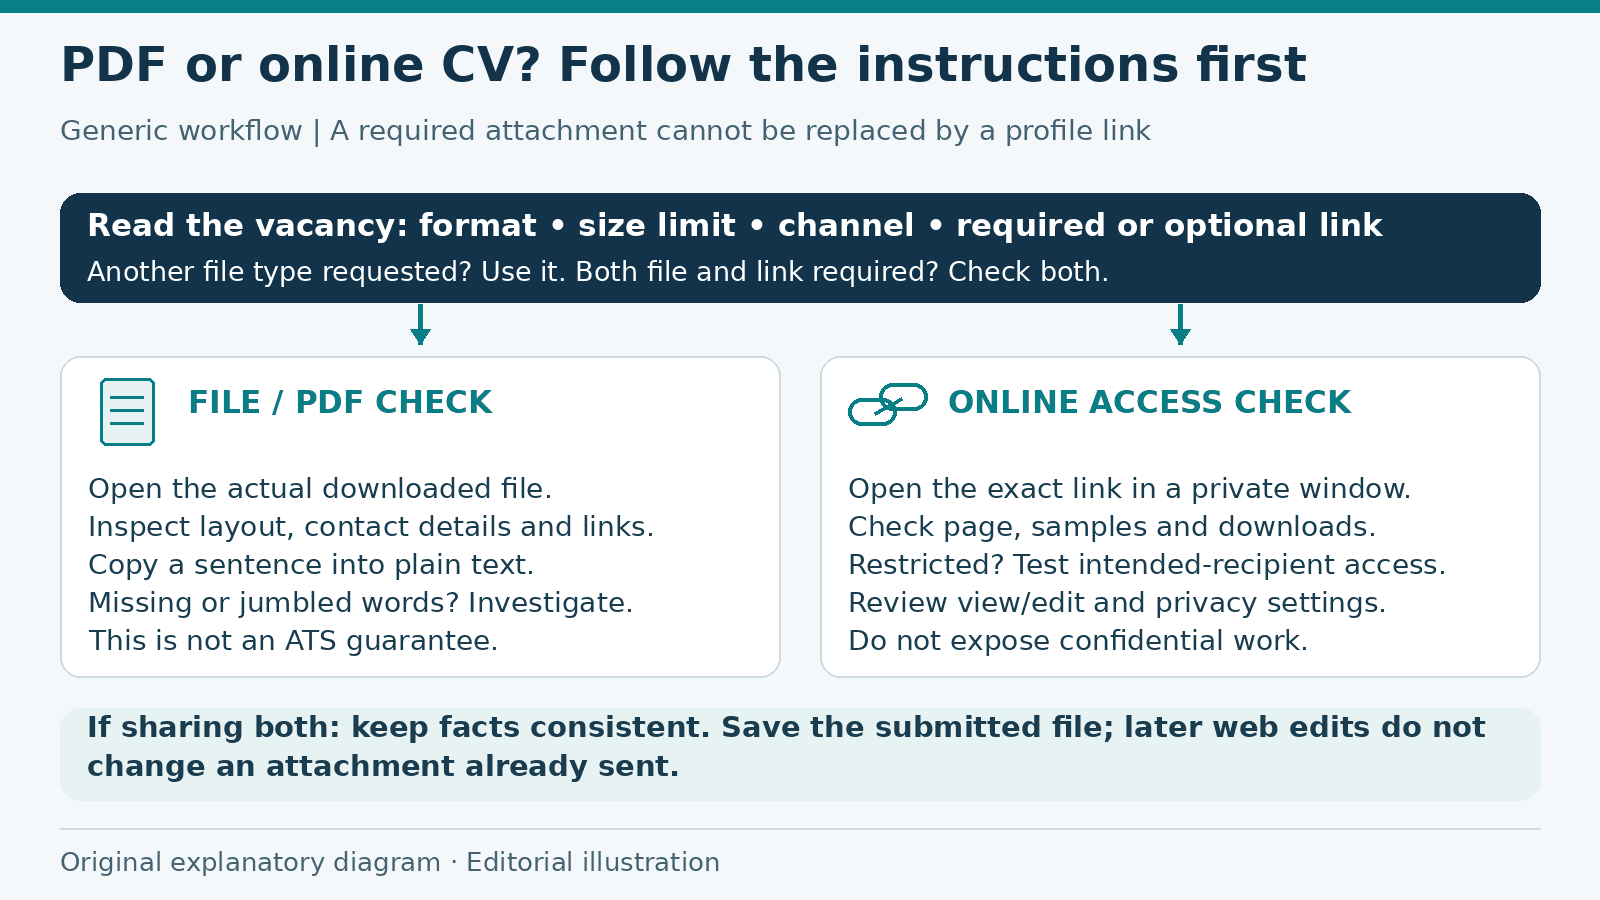
PDF Resume or Online CV: What to Share with Employers
Choose between a PDF resume and an online CV using the employer's instructions, then check readability, permissions, privacy and consistency before sharing.
Read more
Estonia Business Visa Process: EUR 65,000 TRP Route (2026)
Estonia business visa process: lawyer file assessment, EUR 65,000 company route, e-Residency, TRP documents, official fees and arrival planning.
Read moreExplore related career opportunities
Find roles that fit your location and interests. Each listing explains its current or planned vacancies.
All locations, roles and employment types
Comments (0)
Sign in to join the discussion.
No comments yet. Start the conversation.